Skip to content

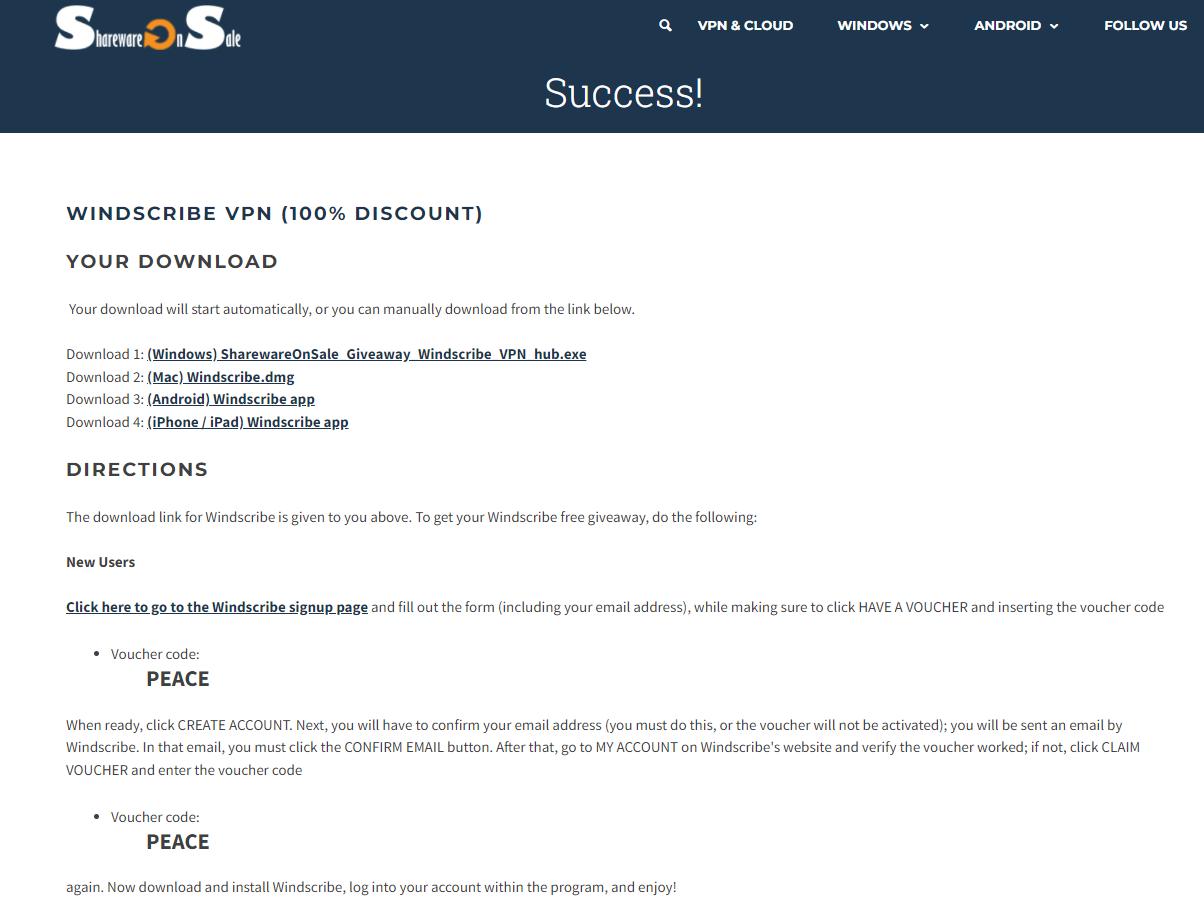
Windscribe VPN offered for free with a lifetime license

General
6 3 3.2k 1

Related Topics
  • Which VPN do you currently use?

    General nord express pia cyber ghost
    6
    4 Votes
    6 Posts
    3k Views
    JAC
    @phenomlab absolutely, their step brother residing in a different Countries. https://surfshark.com/blog/surfshark-vs-nordvpn
  • 3 Votes
    4 Posts
    5k Views
    phenomlab
    I’ve been using this service for a couple of days now, and it’s made my internet access so much faster. That alone is a plus, and I never thought there would be a contender for Cloudflare in this area.
  • Bad information security advice

    Security linkedin security advice
    1
    1
    1 Votes
    1 Posts
    797 Views
    No one has replied
  • Securing javascript -> PHP mysql calls on Website

    Solved Security php mysql security
    2
    1 Votes
    2 Posts
    2k Views
    phenomlab
    @mike-jones Hi Mike, There are multiple answers to this, so I’m going to provide some of the most important ones here JS is a client side library, so you shouldn’t rely on it solely for validation. Any values collected by JS will need to be passed back to the PHP backend for processing, and will need to be fully sanitised first to ensure that your database is not exposed to SQL injection. In order to pass back those values into PHP, you’ll need to use something like <script> var myvalue = $('#id').val(); $(document).ready(function() { $.ajax({ type: "POST", url: "https://myserver/myfile.php?id=" + myvalue, success: function() { $("#targetdiv").load('myfile.php?id=myvalue #targetdiv', function() {}); }, //error: ajaxError }); return false; }); </script> Then collect that with PHP via a POST / GET request such as <?php $myvalue= $_GET['id']; echo "The value is " . $myvalue; ?> Of course, the above is a basic example, but is fully functional. Here, the risk level is low in the sense that you are not attempting to manipulate data, but simply request it. However, this in itself would still be vulnerable to SQL injection attack if the request is not sent as OOP (Object Orientated Programming). Here’s an example of how to get the data safely <?php function getid($theid) { global $db; $stmt = $db->prepare("SELECT *FROM data where id = ?"); $stmt->execute([$theid]); while ($result= $stmt->fetch(PDO::FETCH_ASSOC)){ $name = $result['name']; $address = $result['address']; $zip = $result['zip']; } return array( 'name' => $name, 'address' => $address, 'zip' => $zip ); } ?> Essentially, using the OOP method, we send placeholders rather than actual values. The job of the function is to check the request and automatically sanitise it to ensure we only return what is being asked for, and nothing else. This prevents typical injections such as “AND 1=1” which of course would land up returning everything which isn’t what you want at all for security reasons. When calling the function, you’d simply use <?php echo getid($myvalue); ?> @mike-jones said in Securing javascript -> PHP mysql calls on Website: i am pretty sure the user could just use the path to the php file and just type a web address into the search bar This is correct, although with no parameters, no data would be returned. You can actually prevent the PHP script from being called directly using something like <?php if(!defined('MyConst')) { die('Direct access not permitted'); } ?> then on the pages that you need to include it <?php define('MyConst', TRUE); ?> Obviously, access requests coming directly are not going via your chosen route, therefore, the connection will die because MyConst does not equal TRUE @mike-jones said in Securing javascript -> PHP mysql calls on Website: Would it be enough to just check if the number are a number 1-100 and if the drop down is one of the 5 specific words and then just not run the rest of the code if it doesn’t fit one of those perameters? In my view, no, as this will expose the PHP file to SQL injection attack without any server side checking. Hope this is of some use to start with. Happy to elaborate if you’d like.
  • Why you should never neglect physical security

    Blog infrastructure security blog
    1
    0 Votes
    1 Posts
    1k Views
    No one has replied
  • Changing Passwords Regularly Actually Weakens Security

    Blog security blog
    1
    1
    0 Votes
    1 Posts
    2k Views
    No one has replied
  • Surface Web, Deep Web, And Dark Web Explained

    Blog security blog
    3
    1
    0 Votes
    3 Posts
    3k Views
    phenomlab
    @justoverclock yes, completely understand that. It’s a haven for criminal gangs and literally everything is on the table. Drugs, weapons, money laundering, cyber attacks for rent, and even murder for hire. Nothing it seems is off limits. The dark web is truly a place where the only limitation is the amount you are prepared to spend.
  • Wasting a scammer's time is hugely entertaining

    Blog security blog
    1
    1
    1 Votes
    1 Posts
    1k Views
    No one has replied