Skip to content

Bad information security advice

Security
1 1 804 1
  • wrote on last edited by phenomlab
    #1

    It’s not often that I post anything on LinkedIn, but the post below caught my eye, and raised an eyebrow (to say the least) when I read it.
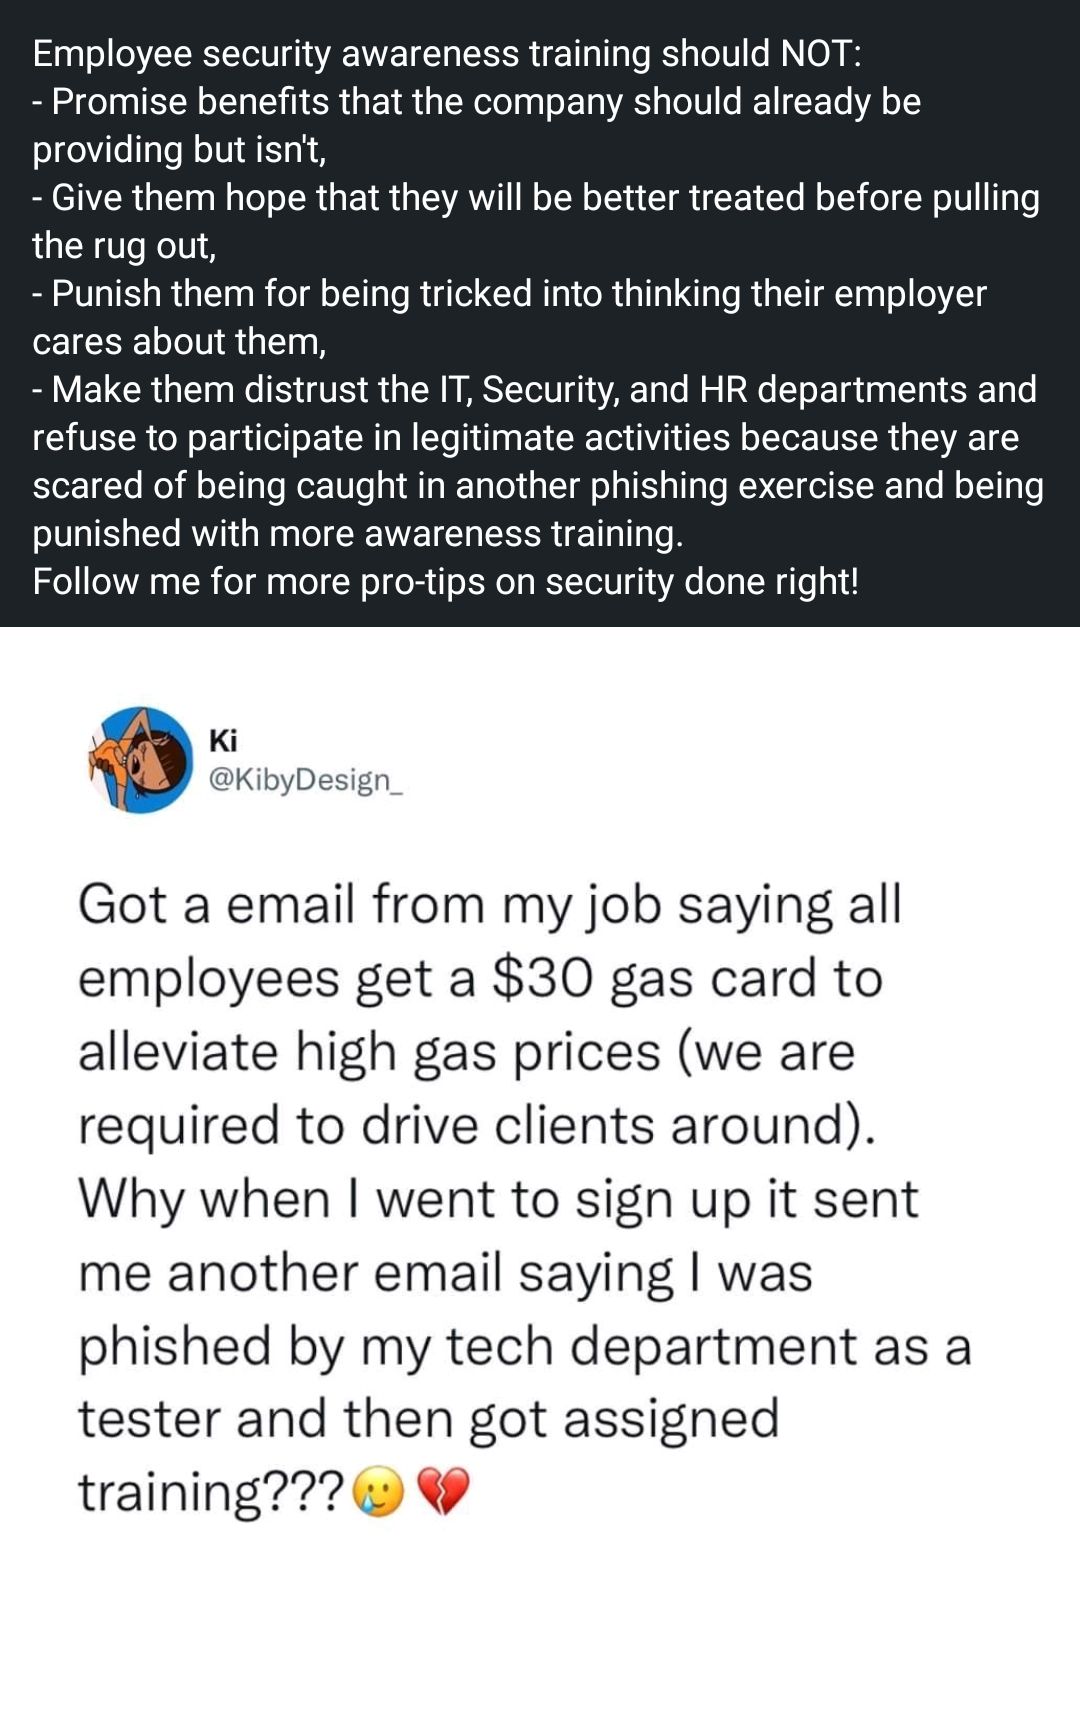
    Screenshot_2023-08-24-20-39-47-54_254de13a4bc8758c9908fff1f73e3725.jpg

    I typically remain impassive and neutral to most of these types of post as they are usually aimed at selling you something. However, the frankly absurd security advice here being offered was so bad, I found it hard to ignore and posted the below response

    Forgive me if I decide not to take any of your cyber security advice as all of the points you’ve raised are the entire point of phishing exercises. Do you really think a nefarious actor isn’t going to send emails that look just like this (mostly because they have succeeded elsewhere as others have highlighted)?

    Your profile states that you are the leader of a world class cyber security team, yet you offer really bad advice like this? This is exactly how all cyber security campaigns work and their effectiveness is blatantly obvious by the screenshot you posted.

    “Hurt feelings” are irrelevant when you are measuring the effectiveness of your cyber security program. As the primary defense in any organization, the security department needs to be in a position to detect and repel as many attacks as possible. The paradigm here being that an organization needs to stop thousands of these attacks getting through per day (probably way more) yet an attacker only needs one link to be clicked for their campaign to succeed.

    Employee security awareness should in fact be everything that the original poster claims it shouldn’t be. Just look at the success rate of previous campaigns which any decent training program is based on.

    The bottom line here is that I really don’t understand the reasoning for the original post. This guy claims to be the leader of a world class cyber security team, yet he decides to give poor advice like this?

    Speechless. And this is a so called professional?? We’re all doomed 😱


Related Topics
  • Claude Mythos in cyber security

    Chitchat security artificial intelligence
    4
    5 Votes
    4 Posts
    2k Views
    phenomlab
    @crazycells I did see something similar to that article, yes. I never fully understood why anyone would want to give unfettered and complete access to AI without first understanding exactly what it had control of, and what it intended to do with that access. This isn’t the first “horror story” and it won’t be the last.
  • 2 Votes
    2 Posts
    1k Views
    phenomlab
    @Muhammad-Abdan-Farooqui Welcome! i’m currently using (and recommend) Bitdefender. For my sins, I’m using Windows, but need this for teams and Office365 integration (otherwise I’d always choose Linux). Have you looked at the Bitdefender product for MAC? https://www.bitdefender.com/en-gb/consumer/antivirus-for-mac
  • 0 Votes
    3 Posts
    1k Views
    phenomlab
    @Madchatthew feel free! You never know
  • Network Security Monitoring

    Learning security network server
    7
    3 Votes
    7 Posts
    3k Views
    Madchatthew
    @phenomlab I will check those out. Thanks for sharing. I appreciate it!
  • 12 Votes
    8 Posts
    9k Views
    phenomlab
    @crazycells good question. Gmail being provided by Google is going to be one of the more secure by default out of the box, although you have to bear in mind that you can have the best security in the world, but that is easily diluted by user decision. Obviously, it makes sense to secure all cloud based services with at least 2fa protection, or better still, biometric if available, but email still remains vastly unprotected (unless enforced in the sense of 2fa, which I know Sendgrid do) because of user choice (in the sense that users will always go for the path of least resistance when it comes to security to make their lives easier). The ultimate side effect of taking this route is being vulnerable to credentials theft via phishing attacks and social engineering. The same principle would easily apply to Proton Mail, who also (from memory) do not enforce 2fa. Based on this fact, neither product is more secure than the other without one form of additional authentication at least being imposed. In terms of direct attack on the servers holding mail accounts themselves, this is a far less common type of attack these days as tricking the user is so much simpler than brute forcing a server where you are very likely to be detected by perimeter security (IDS / IPS etc).
  • 4 Votes
    4 Posts
    2k Views
    JAC
    @phenomlab said in TikTok fined £12.7m for misusing children’s data: Just another reason not to use TikTok. Zero privacy, Zero respect for privacy, and Zero controls in place. https://news.sky.com/story/tiktok-fined-12-7m-for-data-protection-breaches-12849702 The quote from this article says it all TikTok should have known better. TikTok should have done better They should have, but didn’t. Clearly the same distinct lack of core values as Facebook. Profit first, privacy… well, maybe. Wow, that’s crazy! so glad I stayed away from it, rotten to the core.
  • Secure SSH connectivty

    Security ssh keys security
    7
    6 Votes
    7 Posts
    3k Views
    DownPW
    @phenomlab yep but I use it since several month and I haven’t see any bugs or crash In any case, I only use him anymore Tabby offers tabs and a panel system, but also themes, plugins and color palettes to allow you to push the experience to the limit. It can support different shells in the same window, offers completion, has an encrypted container for your passwords, SSH keys and other secrets, and can handle different connection profiles. Each tab is persistent (you can restore them if you close one by mistake) and has a notification system, which will let you know if, for example, a process is finished while you are tapping in another tab. It’s really a great terminal that will easily replace cmd.exe for Windowsians or your usual terminal. And it can even work in a portable version for those who like to carry their tools on a USB key. –> To test it, you can download it, but there is also a web version. Handy for getting an idea. https://app.tabby.sh
  • is my DMARC configured correctly?

    Solved Configure
    3
    2
    3 Votes
    3 Posts
    2k Views
    Hari
    @phenomlab said in is my DMARC configured correctly?: you’ll get one from every domain that receives email from yours. Today I have received another mail from outlook DMARC, i was referring to your reply again and found it very helpful/informative. thanks again. I wish sudonix 100 more great years ahead!