Skip to content

TikTok fined £12.7m for misusing children's data

Discussion
4 3 1.8k 1

Related Topics
  • 2 Votes
    2 Posts
    1k Views
    phenomlab
    @Muhammad-Abdan-Farooqui Welcome! i’m currently using (and recommend) Bitdefender. For my sins, I’m using Windows, but need this for teams and Office365 integration (otherwise I’d always choose Linux). Have you looked at the Bitdefender product for MAC? https://www.bitdefender.com/en-gb/consumer/antivirus-for-mac
  • Microsoft in talks to buy TikTok

    Discussion microsoft tiktok
    2
    3 Votes
    2 Posts
    932 Views
    Madchatthew
    @phenomlab well I hope that a better company steps up and puts in a higher bid. If I had the money I would buy TikTok. That platform is a money makers dream. So many people on it now er or was. I think MS will just mess it up like they do everything else. Hell, they can’t even get their own software to work correctly, how would they even keep that one up and running.
  • 2 Votes
    4 Posts
    2k Views
    phenomlab
    @DownPW This won’t be the first time that Amazon and others like them are being bought to account. I recall seeing a documentary on the TV recently where they sent in a reporter with secret cameras to film the strict regimen and constant threat of being fired for not meeting targets that workers are placed under. The surveillance just takes this to a whole new level in my view and it’s like being placed under a microscope for constant scrutiny. This goes well beyond the surveillance placed on prisoners!
  • 4 Votes
    7 Posts
    3k Views
    crazycells
    @phenomlab oh no, that is 1 cent on the video, but you are right, symbols are similar… I just converted it to $1 , since it is more intuitive in daily life…
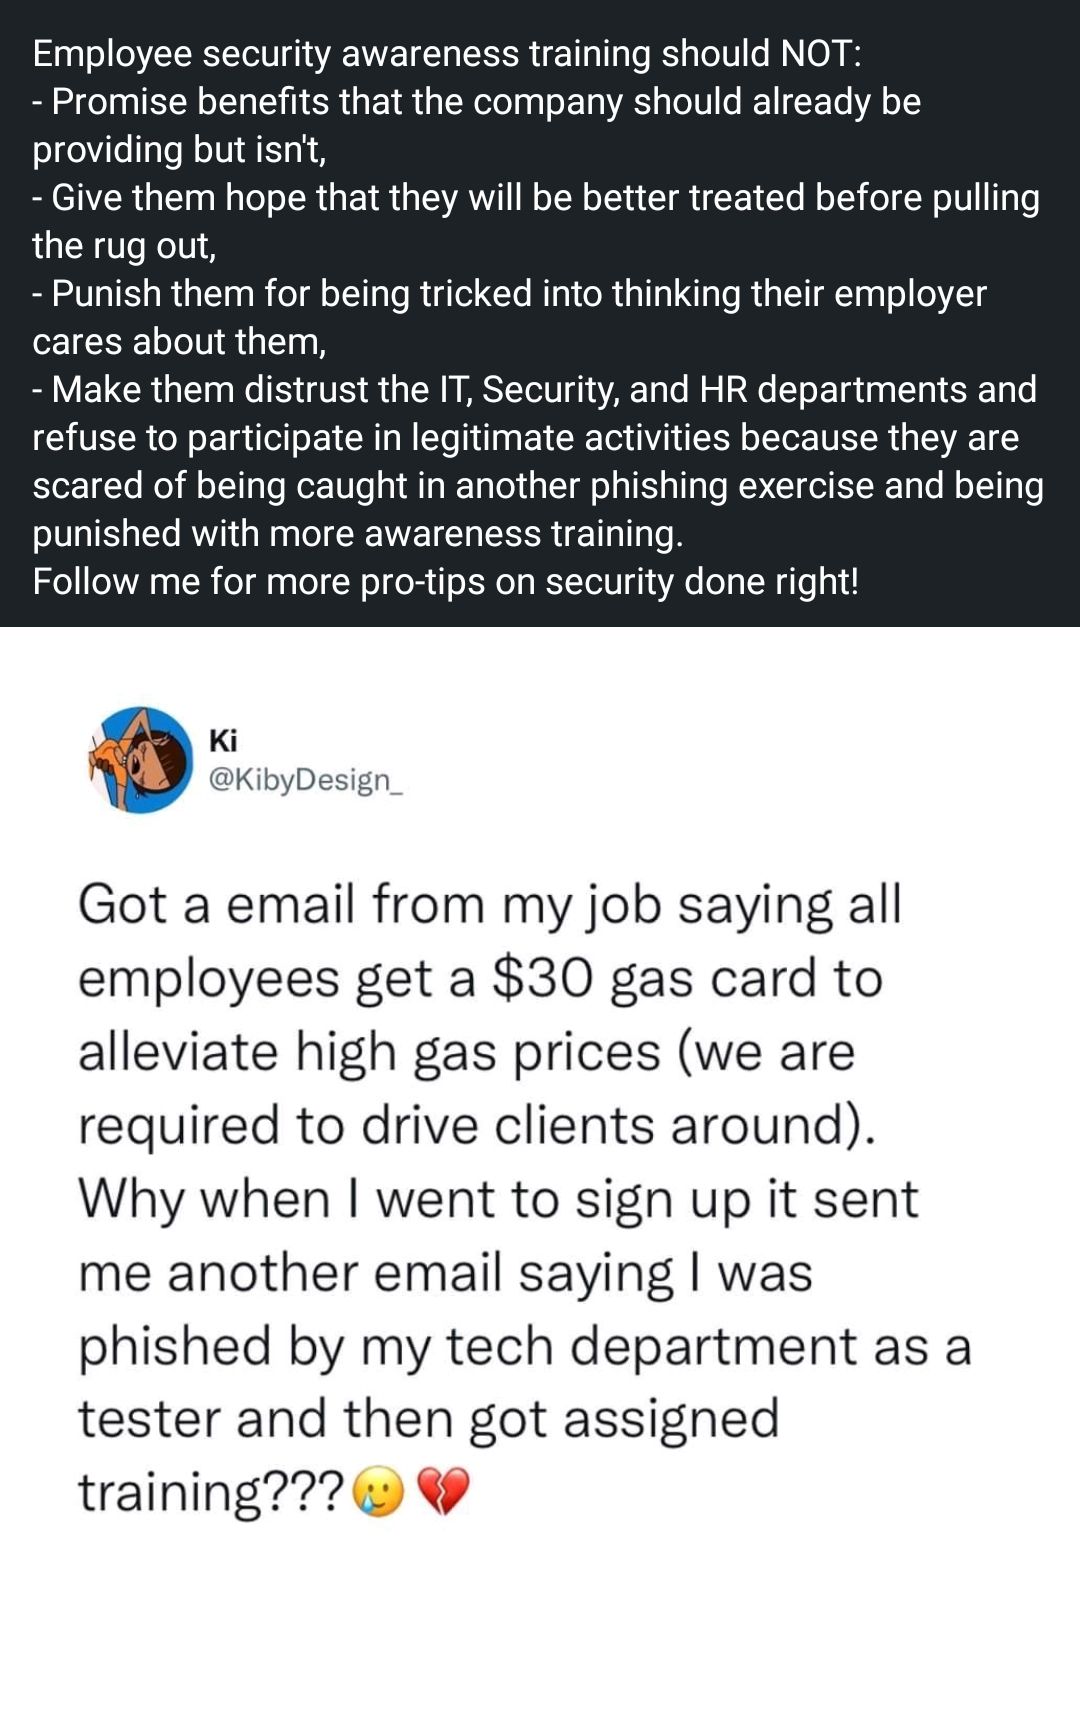
  • Bad information security advice

    Security linkedin security advice
    1
    1
    1 Votes
    1 Posts
    804 Views
    No one has replied
  • 0 Votes
    4 Posts
    2k Views
    phenomlab
    @DownPW most of this really depends on your desired security model. In all cases with firewalls, less is always more, although it’s never as clear cut as that, and there are always bespoke ports you’ll need to open periodically. Heztner’s DDoS protection is superior, and I know they have invested a lot of time, effort, and money into making it extremely effective. However, if you consider that the largest ever DDoS attack hit Cloudflare at 71m rps (and they were able to deflect it), and each attack can last anywhere between 8-24 hours which really depends on how determined the attacker(s) is/are, you can never be fully prepared - nor can you trace it’s true origin. DDoS attacks by their nature (Distributed Denial of Service) are conducted by large numbers of devices whom have become part of a “bot army” - and in most cases, the owners of these devices are blissfully unaware that they have been attacked and are under command and control from a nefarious resource. Given that the attacks originate from multiple sources, this allows the real attacker to observe from a distance whilst concealing their own identity and origin in the process. If you consider the desired effect of DDoS, it is not an attempt to access ports that are typically closed, but to flood (and eventually overwhelm) the target (such as a website) with millions of requests per second in an attempt to force it offline. Victims of DDoS attacks are often financial services for example, with either extortion or financial gain being the primary objective - in other words, pay for the originator to stop the attack. It’s even possible to get DDoS as a service these days - with a credit card, a few clicks of a mouse and a target IP, you can have your own proxy campaign running in minutes which typically involves “booters” or “stressers” - see below for more https://heimdalsecurity.com/blog/ddos-as-a-service-attacks-what-are-they-and-how-do-they-work @DownPW said in Setting for high load and prevent DDoS (sysctl, iptables, crowdsec or other): in short if you have any advice to give to secure the best. It’s not just about DDos or firewalls. There are a number of vulnerabilities on all systems that if not patched, will expose that same system to exploit. One of my favourite online testers which does a lot more than most basic ones is below https://www.immuniweb.com/websec/ I’d start with the findings reported here and use that to branch outwards.
  • Why you should never neglect physical security

    Blog infrastructure security blog
    1
    0 Votes
    1 Posts
    1k Views
    No one has replied
  • Security, Or Just Obscurity?

    Blog security blog
    1
    1
    0 Votes
    1 Posts
    1k Views
    No one has replied