Skip to content

Setting up Ghost DIgitalOcean droplet with cloudflare

General
11 2 3.6k 1
  • wrote on last edited by
    #1

    Hi, hope you are doing great. 🙂

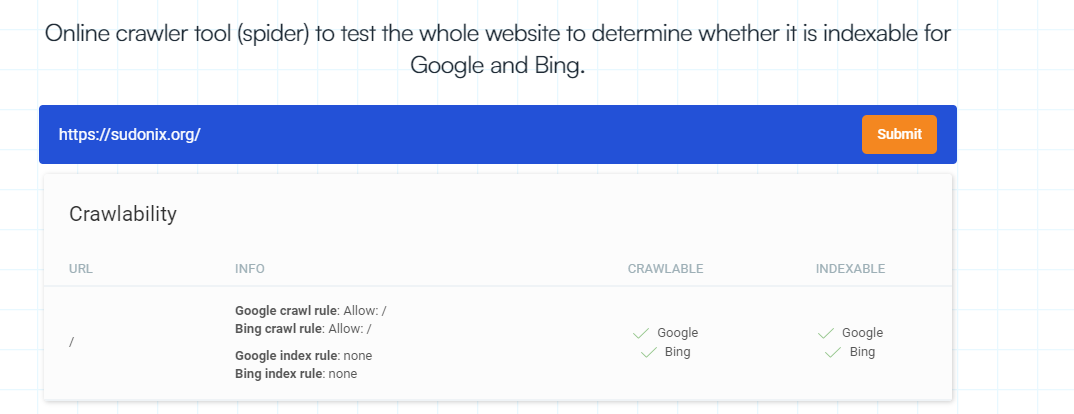
    I’m trying to configure Ghost, and after the installation, Ghost is functional. However, after 10min, it enters a redirection loop. I’m unsure whether the issue lies with Cloudflare, Ghost, or Ghost’s private mode. I would appreciate any insights you can provide on this matter.

  • wrote on last edited by
    #2
  • Hi, hope you are doing great. 🙂

    I’m trying to configure Ghost, and after the installation, Ghost is functional. However, after 10min, it enters a redirection loop. I’m unsure whether the issue lies with Cloudflare, Ghost, or Ghost’s private mode. I would appreciate any insights you can provide on this matter.

    wrote on last edited by
    #3

    @Hari what is being displayed in the console?

  • @Hari what is being displayed in the console?

    wrote on last edited by
    #4

    @phenomlab idk, i think the issue with CF always SSL setting. i had to turn it off and let the nginx handle http>https . not sure this is safe approach or not for now the site is in under construction mode with ghost. we might move to ghost in 6 months the migration is the big task. wordpress and ghost both have their own pros and cons 😢

  • @phenomlab idk, i think the issue with CF always SSL setting. i had to turn it off and let the nginx handle http>https . not sure this is safe approach or not for now the site is in under construction mode with ghost. we might move to ghost in 6 months the migration is the big task. wordpress and ghost both have their own pros and cons 😢

    wrote on last edited by
    #5

    @Hari I would anyways have nginx handle the redirect between http and https anyway.

  • @Hari I would anyways have nginx handle the redirect between http and https anyway.

    wrote on last edited by
    #6

    @phenomlab New query: I’m attempting to install multiple instances of Ghost on a single droplet. I’ve completed the initial setup using the 1-click Digital Ocean setup as outlined in the following guide:

    https://forum.ghost.org/t/ghost-tips-tricks-12-install-multiple-ghost-installations-on-digitalocean/24723#create-a-website-directory-for-example-ubud-2

    However, while following the instructions in the above guide, I encountered an issue with the MySQL root passwords. I’m unsure about what went wrong, and I’m unable to determine the current MySQL root password. I’ve tried several commands found online, but none have been successful. Any suggestions? Please advise.

  • wrote on last edited by
    #7

    i have tried figuring out the root passwords and i could not do it. now going for a fresh ubutu droplet

  • wrote on last edited by
    #8

    I have found ways to properly modify root passowrd here, going with old droplet now 😄

    https://vegastack.com/tutorials/how-to-install-ghost-on-ubuntu-22-04/

  • I have found ways to properly modify root passowrd here, going with old droplet now 😄

    https://vegastack.com/tutorials/how-to-install-ghost-on-ubuntu-22-04/

    wrote on last edited by
    #9

    @Hari Interested to know how you got on with the GHOST journey 🙂

  • @Hari Interested to know how you got on with the GHOST journey 🙂

    wrote on last edited by
    #10

    @phenomlab It is all because of a theme 😄

  • @phenomlab It is all because of a theme 😄

    wrote on last edited by
    #11

    @Hari Really? Can you elaborate a bit more here?


Related Topics
  • 4 Votes
    3 Posts
    2k Views
    crazycells
    thanks @DownPW ! this is definitely very helpful.
  • Ubuntu 22.04 to Ubuntu 24.04 Unable to ping

    Locked Unsolved Linux ubuntu
    37
    3 Votes
    37 Posts
    14k Views
    abcabc123
    Okay, you have time, let me know
  • Cloudflare bot fight mode and Google search

    Blog cloudflare crawler indexing
    12
    2
    10 Votes
    12 Posts
    6k Views
    phenomlab
    @veronikya said in Cloudflare bot fight mode and Google search: docker modifications are a pain in the ass, I couldn’t have put that better myself - such an accurate analogy. I too have “been there” with this pain factor, and I swore I’d never do it again.
  • 4 Votes
    8 Posts
    5k Views
    WesleyMoura
    @phenomlab Sorry to delay in responding, yes as i mentioned above, i had to remove my redis from docker and reinstall a new image with this command docker run --name=redis -p 127.0.0.1:6379:6379 -d -t redis:alpine and now when i test my ip and port on https://www.yougetsignal.com/tools/open-ports/ the status of my redis port is closed. I think which to configure firewall in droplet digital ocean is a good idea too, and i will configure soon. Thanks for the help!
  • Virtualmin Setup DigitalOcean

    Solved Customisation virtualmin digitalocean
    26
    9 Votes
    26 Posts
    13k Views
    phenomlab
    @Hari said in Virtualmin Setup DigitalOcean: i have felt it is very hard to manage Virtualmin the settings are confusing It’s a bit of a learning curve, admittedly, but very powerful and easy to use provided you understand the implications of what you are doing. For example, moving a VirtualMin server to subserver and then back again without changing underlying components that rely on the correct placement of the server, of course it will no longer work.
  • how to use CF tunnels with Virtualmin?

    Solved Configure cf tunnel cloudflare virtualmin
    10
    3 Votes
    10 Posts
    4k Views
    phenomlab
    @Hari DDoS protection is not just a switch, or one component. It’s a collection of different and often disparate technologies that when grouped together form the basis of a combined toolset that can be used in defence. Typically these consist of IDS (Instrusion Detection System) and IPS (Intrusion Prevention System) components that detect irregularities in network traffic, and will take decisive action based on predefined rulesets, or in the case of more modern systems, AI and ML. Traditional “traffic shaping” technology is also deployed, so if an attack cannot be easily identified as malicious, the bandwidth available to that connection is severely limited to nothing more than a trickle rather than a full flow. Years ago, ISP’s used traffic shaping (also called “policers”) as an effective means of stopping applications such as BearShare, eDonkey, Napster, and other P2P based sharing systems from functioning correctly - essentially reducing the “appeal” of distributing and seeding illegal downloads. This was essentially the ISP’s way of saying “stop what you are doing please” without actually pulling the plug. These days, DDoS attacks are designed to overwhelm - not assume control of - webservers and other public facing components. It’s rare for small entities to be attacked unless there is some form of political agenda driven by your site or product. A classic example is governmental institutions or lawmakers who effectively are classed as “enforcers” and those who disagree are effectively making a statement in the form of Denial of Service. DDoS protection is effectively the responsibility of the hosting provider, but you shouldn’t just assume that they will protect you or your site. Their responsibility stops at their infrastructure, so it’s then up to you too decide how you full the gap in between your host and the website. Typically, you’d leverage something like Imunify360 which you can get for Plesk (and something I’d strongly recommend) but it’s not free, and is a paid (not expensive per month) subscription. If you want to use VirtualMin then there are a variety of tools readily available out of the box such as firewalls and fail2ban.
  • Any improvement on Ghost addon?

    Solved Configure ghost blog
    6
    2 Votes
    6 Posts
    3k Views
    phenomlab
    @kurulumu-net CSS styling is now addressed and completed.
  • Digitalocean Ubuntu configuration

    Solved Linux
    33
    12 Votes
    33 Posts
    15k Views
    justoverclock
    @phenomlab thank you! not me